Amadeus data breach exposes 53,000 Cathay Pacific bookings
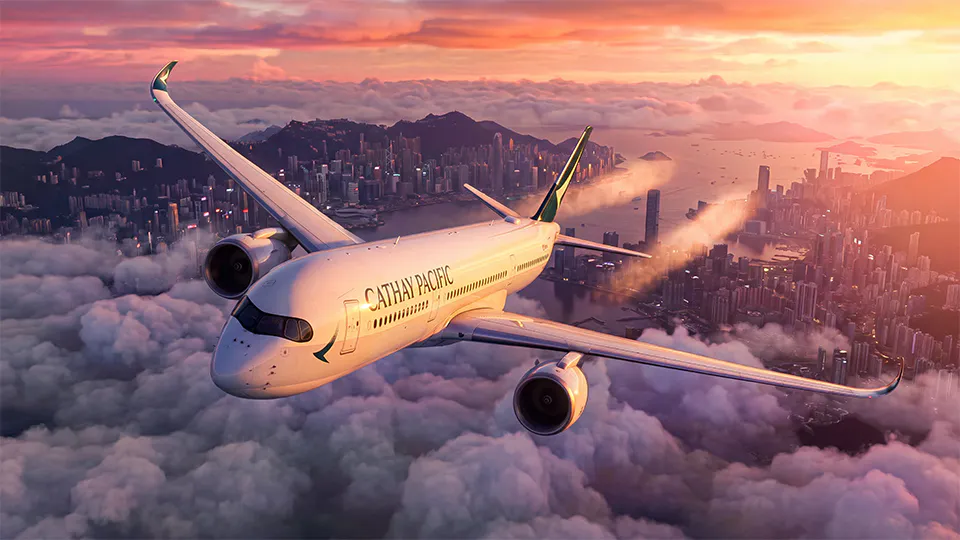
The Hong Kong-based
carrier said on October 30 that the incident exposed booking information,
including reservation references, passenger names and flight details in most
cases. A smaller number of bookings involved additional personal information.
According to Cathay
Pacific, the affected reservations dated from August 2023 through September
2026, based on information provided by Amadeus.
The airline said there
was no evidence that financial or payment details had been accessed. It also
confirmed that its own systems and flight operations were not affected by the
breach.
Cathay Pacific said
Amadeus had taken steps to contain the incident and introduced stronger system
monitoring and threat detection measures.
Amadeus previously
acknowledged identifying a vulnerability in a travel booking display
environment. The company said investigations were continuing and that there was
no indication the vulnerability had been exploited for ransomware attacks. It
did not disclose how many airlines or customers were affected.
The incident has also
prompted disclosures from other carriers. Japan Airlines recently reported that
unauthorized access to an Amadeus system exposed information belonging to
approximately 92,000 customers. South Korea's Asiana Airlines has also reported
compromised customer data linked to the breach.