Malaysia Airlines says customer data may be hit in Amadeus breach
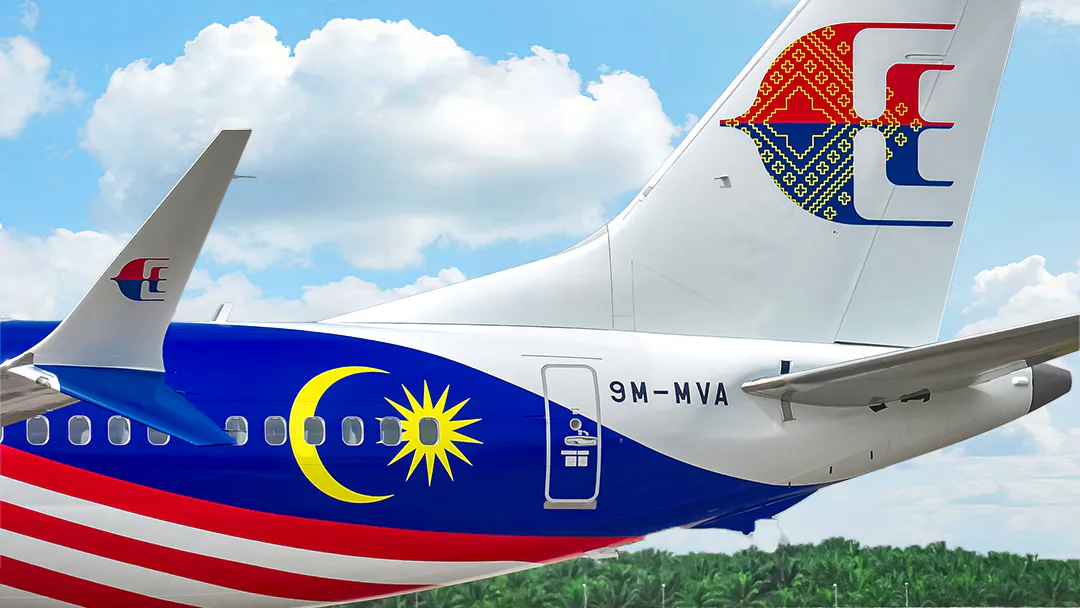
Dhaka: Malaysia Airlines has warned customers of possible data exposure in the recently disclosed cybersecurity incident at Amadeus, its third-party airline reservation technology provider.
An official statement from the airline said the incident may have affected customer information processed through Amadeus between August 2023 and September 2026.
The Malaysian flag carrier said its own IT systems have not been compromised, adding that there is currently no evidence that financial information has been accessed.
The airline is working closely with Amadeus and relevant parties to investigate the incident and assess its impact. It did not disclose how many customers may be affected or what types of data were involved.
As a precaution, Malaysia Airlines urged customers to remain vigilant against suspicious or unsolicited communications, particularly those requesting personal or financial information.
The carrier said it will provide further updates as more information becomes available.
Spanish travel technology company Amadeus reported in October that it suffered unauthorized access to its passenger reservation systems. The incident affected several airlines, primarily in the Asia-Pacific region.
Japan Airlines said about 92,000 customers may have been affected, while Cathay Pacific reported around 53,000 bookings. Korean Air and Asiana Airlines have also reported unauthorized access.
Cathay Pacific said an unauthorized party used login credentials assigned to an Amadeus system account and, in most cases, accessed booking references, passenger names, and flight details.
Amadeus said it has contained the incident through a password reset and enhanced monitoring and has found no evidence of data misuse so far.